Install Safe
  • Blog
  • How it works
  • Pricing
  • Free scanner
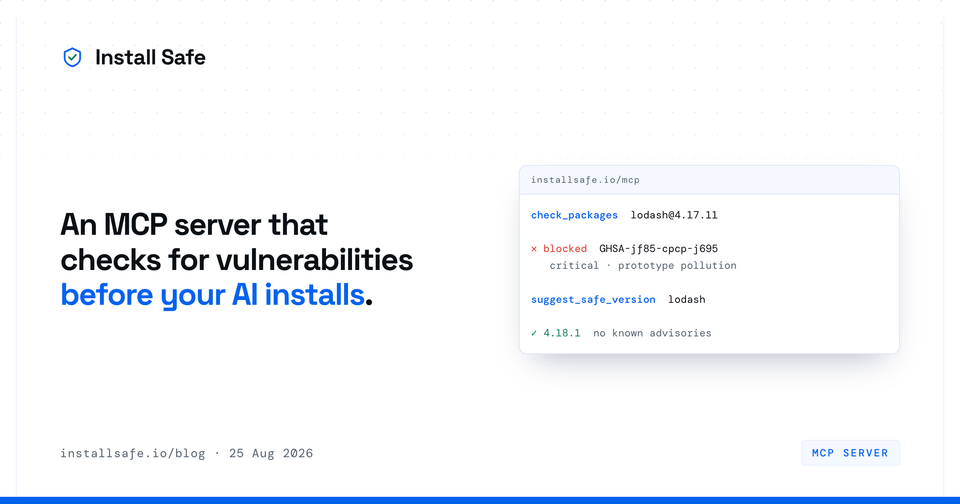
An MCP Server That Checks npm Packages Before Your Agent Installs Them
npm security

An MCP Server That Checks npm Packages Before Your Agent Installs Them

Your coding agent can now ask whether an npm package has known advisories before it installs it. An anonymous MCP server at installsafe.io/mcp, three tools, no API key.
Read more
Prasanna Mestha
JFrog Xray Alternative for npm Supply-Chain Security (2026)
supply chain security

JFrog Xray Alternative for npm Supply-Chain Security (2026)

JFrog Xray + Curation is powerful but means adopting Artifactory and an enterprise contract. Here's an honest comparison with a drop-in npm registry firewall that blocks malicious packages across CI and AI agents.
Read more
Prasanna Mestha
Malicious npm Packages Deploy RedShell (RedC2): Check If You're Exposed
npm security

Malicious npm Packages Deploy RedShell (RedC2): Check If You're Exposed

A new campaign (Aug 24, 2026) hides the RedShell RedC2 Linux implant inside decoy "streak"/"map"/"calc" npm packages. Which packages are affected, how to check if you're exposed, and how to remediate.
Read more
Prasanna Mestha
Dependabot Alternative for npm Supply-Chain Security (2026)
npm-security

Dependabot Alternative for npm Supply-Chain Security (2026)

Dependabot alerts and opens PRs after an advisory lands — it doesn't stop the install. See how a hosted npm registry firewall blocks bad versions across CI, Docker and AI agents with two config lines, and why you run both together.
Read more
Prasanna Mestha
npm audit Alternative: Block Malware, Not Just Known CVEs
npm-security

npm audit Alternative: Block Malware, Not Just Known CVEs

npm audit reports known CVEs after you've already installed. It can't see malware — the exact threat behind 2026's npm worms. Here's what a real npm audit alternative does, and how to block bad versions at the registry with two config lines.
Read more
Prasanna Mestha
JSONata's critical RCE: one expression opens a shell
supply chain security

JSONata's critical RCE: one expression opens a shell

The patches shipped back in May and July — but the three critical JSONata RCE CVEs only went public on Aug 21, so plenty of teams have been quietly exposed without knowing. Which versions are affected, how to find them in your lockfile, and how to fix it.
Read more
Prasanna Mestha
Aikido Safe Chain Alternative: Best Options for npm
npm security

Aikido Safe Chain Alternative: Best Options for npm

A practical Aikido Safe Chain alternative comparison covering npm malware checks, package-age controls, behavioral analysis, CI, and registry enforcement.
Read more
Prasanna Mestha
A Tool to Block AI From Installing Malicious npm Packages
npm security

A Tool to Block AI From Installing Malicious npm Packages

AI coding agents install hallucinated and slopsquatted npm packages without blinking. Here's how to block AI from installing malicious npm packages at the registry, with two config lines (registry URL and token).
Read more
Prasanna Mestha
Sonatype Nexus Firewall Alternative for npm
supply chain security

Sonatype Nexus Firewall Alternative for npm

Sonatype Nexus Firewall (Repository Firewall) vs a drop-in npm registry firewall — an honest comparison of detection, cost, and setup, plus how to switch.
Read more
Prasanna Mestha
Snyk Alternative for npm Supply-Chain Security
npm security

Snyk Alternative for npm Supply-Chain Security

Snyk scans and alerts — it doesn't block installs. See how InstallSafe's registry firewall compares to Snyk, Socket, Aikido and Dependabot, and when to use each.
Read more
Prasanna Mestha
Socket.dev Alternative: Registry-Level npm Security
npm security

Socket.dev Alternative: Registry-Level npm Security

Socket.dev is strong at zero-hour behavioral detection — but it scans PRs, not installs. See how InstallSafe's registry firewall, Snyk, and Aikido compare, and when to use each.
Read more
Prasanna Mestha
The keyv worm ate 400+ npm packages in 90 minutes — check if you're exposed
supply chain security

The keyv worm ate 400+ npm packages in 90 minutes — check if you're exposed

A self-replicating npm worm hit keyv and 400+ packages in 90 minutes, stealing cloud, GitHub, and AI-agent credentials during install. Here's how to check your tree — and why install-time blocking is the only real defense.
Read more
Prasanna Mestha
Install Safe © 2026
  • Scan your project
  • installsafe.io
Powered by Ghost